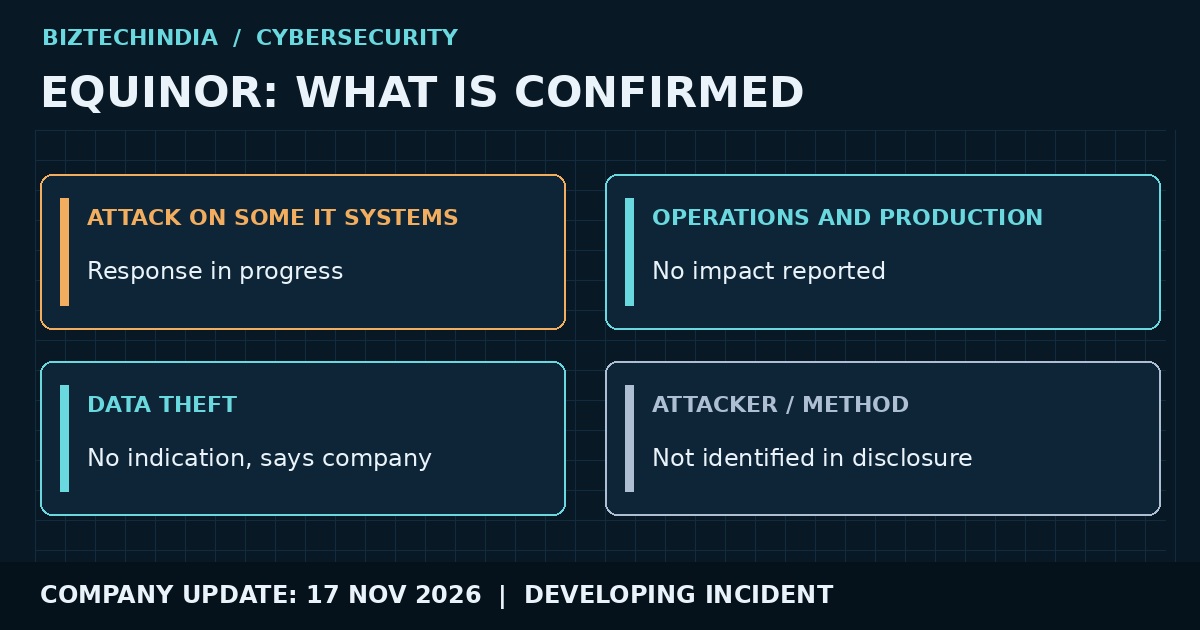
Equinor says it has detected an ongoing cyberattack against some of its IT systems. The important boundary in the Norwegian energy company’s 17 November update is that it reported no effect on operations or production, and no indication that data had been stolen.
Those statements describe the company’s assessment at the time of the update. They do not mean that the incident is over. Equinor said it had mobilised resources to neutralise the attack and restore the full integrity of its systems, and that relevant authorities were being informed.
What has actually been confirmed?
The confirmed disclosure is an attack affecting certain IT systems. Equinor did not identify those systems in its short public statement, name an attacker or describe the route used to gain access. It also did not announce a timetable for completing the response.
Reuters separately reported the company’s disclosure. Neither the company statement nor that report establishes ransomware, a payment demand, a specific stolen dataset or responsibility by a particular country or group. Adding any of those details would go beyond the available evidence.
An IT incident is not the same as a production outage
A cyberattack disclosure, theft of information and disruption to physical operations are different claims. One can be confirmed while the others are not. In this case, Equinor explicitly said the attack had not affected its operations or production.
That is why an attack headline should not be rewritten as an oil or gas supply shutdown. Equally, continued production does not make the security incident immaterial: the company was still working to neutralise the attack and restore system integrity.
Read the data-theft statement carefully
Equinor’s statement that there was no indication of stolen data is an evidence-based status report, not a guarantee about what a completed investigation will find. It should not be turned into either a confirmed leak or a declaration that every possible risk has been ruled out.
The next useful disclosures would be confirmation that the attack has been contained, clarification of the affected systems, any change in the data-theft assessment, and any effect on operations. Equinor said it would provide updates when new information becomes available.
Do not join unrelated incidents without evidence
The timing of a cyberattack alongside other technology problems does not establish a common cause. This disclosure supplies no basis to connect Equinor’s incident to outages at other organisations. Attribution requires evidence, not a list of headlines published on the same day.
For now, the accurate summary is narrow: an ongoing attack on some IT systems, a response in progress, no reported operational or production impact, and no indication of data theft in the company’s latest statement reviewed for this article. It is not a confirmed supply disruption or an attributed attack.
Reporting basis: Equinor’s 17 November 2026 company update and Reuters reporting. The incident remains developing. Image: original editorial diagram, not a screenshot of Equinor’s systems or a reconstruction of the attack.